I got linked to this video the other day and I can officially say that my brain just crawled out my ear. The video’s a very very simple way of seperating eggs, something I’m sure some protein-sucking egg-yolk hating friends of mine will love!
[Read More]If you want to know how not to do AJAX…
Check out http://www.sccm-tools.com/ in Google Chrome. I’m not quite sure how it works just yet, but it’s certainly spectacular. Every second or so, it grabs a gradually larger and larger request in a runaway fashion.
I have a feeling it has something to do with storing the state of the page or something in its source, but wow. After three minutes, it’s doing 60KB/s.

Want to know how I found this? I left it open for a few MONTHS on my work PC and showed up as an incredibly huge user of bandwidth. Whoops!
[Read More]New Ruger Revolver Announced – the Single-9
A media release from Ruger on a new revolver they’re adding to their lineup:
Sturm, Ruger & Company, Inc. is proud to announce the Ruger® Single-Nine™, a nine-shot, single-action revolver chambered in .22 Winchester Magnum.
The Single-Nine™ features a nine-shot cylinder and is constructed from durable satin-finished stainless steel. With a 6.5-inch barrel and smooth, hardwood, “Gunfighter” grips, the Single-Nine™ is well-balanced and points easily. Williams™ fiber optic sights, click-adjustable for both windage and elevation, provide a crisp sight picture that is enhanced with front and rear fiber optic inserts.
[Read More]
Brad builds Angelina her own Shooting Range
Love is…
Brad Pitt spent nearly USD $400k to build a shooting range/armoury for Angelina Jolie, at the couple’s Miraval estate in southern France, according to The Sun.
A source said: “Brad had a lot to live up with his wedding gift considering Angelina exchanged vials of blood with her ex-husband Billy-Bob Thornton.
“And by letting Angelina de-stress at the range, he’s less likely to get earache indoors. There’s a lot to be said for that when you have six kids.”
[Read More]Form 4473 overlay – interesting idea
In Queensland we have the PTA, and in America they’ve got the Form 4473. Both do similar things - keep a record of firearms transactions. The American National Shooting Sports Foundation has produced an overlay for this form, which makes it easier for people to complete the form correctly.
They’ve just released a new version of the overlay which suits the newly updated version of the form 4473 in the United States.
I wonder if this is something that could be useful for Queensland firearms dealers? I suppose there aren’t that many, so they’ll be proficient in helping people complete their Form 28’s. Something to think about anyhow.
[Read More]LockKill – a novel way to secure a lock
If you’re a property owner or landlord who needs to disable a lock without having to contact a locksmith, I’d say LockKill would be a fantastic solution to the problem.
With a simple design which covers the two main locking mechanisms on the market, it secures itself into the lock by working with the mechanisms that are our normal pin-and-tumbler locking systems. Once in there, it’s almost impossible to remove without professional tools (or destructive measures) and there’s even a small section cut out of the bow of the key which allows for instant and clean removal of the key head.
[Read More]I love purchase suggestions
A great one from Fishpond. I’ve only ever bought one of the science books from them, and I was a little puzzled by one of their suggestions.

Laser Pointers for Queensland Firearms Users
Taken from the information page here on the Qld Police site.
As of 2 April 2012, laser pointers with a power output of greater than 1 milliwatt (1mw) will be restricted items requiring reasonable excuse for lawful possession thereof.
‘Reasonable excuse’ for possession of a laser pointer includes: Firearms Licence holders.
“The person holds a licence that authorises possession of a firearm in relation to which the laser pointer may be used, and the laser pointer has a power output of less than 10 milliwatts.” (10mw)
[Read More]
Upcoming changes to Qld Weapons Licence Cards
According to this article on WLB’s news page, they’re changing the format of new licences. It’s nice to see they’re putting some security features into the card.
Previously I think you could probably have printed them out on any ID card printer, making it much easier to make illicit purchases of ammunition and other goods.
Additional features will include:
- Clear core centre panel depicting the licence number and category of weapons
- Raised embossed date of birth of the licensee at the bottom of the licensee’s photograph
- Expiry Date of the licence on the rear of the card in extra large font
Updating SCOM 2007 R2 Agent Certificates
If you’re attempting to monitor servers that aren’t on the same domain as your Root Management Server you need certificate-based authentication to allow communication between hosts.
There are plenty of articles on how to setup a Certification Authority, we’re running a standard Windows 2008 setup.
Here’s our Standard Operations Procedure for replacing certificates on agents.
- Login with MSTSC to the server requiring the new certificate
- NOTE: When you login, if you’re given a temporary profile it won’t work.
- Open
https://[your root ca]/certsrv/in a web browser - Click on continue if you get a https certificate error
- Go to internet options -> Security -> click on trusted sites
- Click on Sites
- It should have
https://[your root ca]in theAdd this website to the zonefield - Click Add
- Click Close
- On the web page click
Download a CA Certificate, certificate chain or CRL - You’ll probably get another https signing error, ignore it.
- Ensure:
- CA Certificate has the entry with
Currenthighlighted - Encoding method is
DER.
- CA Certificate has the entry with
- Click
Download a CA Certificate - Save the Root CA Certificate somewhere and double click on it to open the key file.
- Ensure the details look right for your Root CA and click
Install certificateon the general page - Click Next
- Select
Place all certificates in the following storeand click browse - Select
Trusted Root Certification Authoritiesand click OK, then next and Finish. - It’ll warn you about an un-validated certificate, click yes.
- The root CA trust certificate is installed
- In the browser click
Homein the top right - Click
Request a certificate - Click
Advanced certificate request - Click
Create and submit a request to this CA - Fill in the fields as below Name = FQDN of client Type = Other OID = 1.3.6.1.5.5.7.3.1,1.3.6.1.5.5.7.3.2 Create new Key Set CSP = Microsoft Enhanced Cryptographic Provider v1.0 Key usage = Both Key Size = 1024 Automatic key container name Mark keys as exportable = tick Request format = CMC Hash = sha1 Friendly name = FQDN of client (must match first field)
- Click submit
- It may confirm that you wish to request a new certificate, click yes.
- You’ll be issued a request ID.
- Login to the certificate server and open Certificate Authority from Administrative Tools
- Expand the tree and find Pending Requests
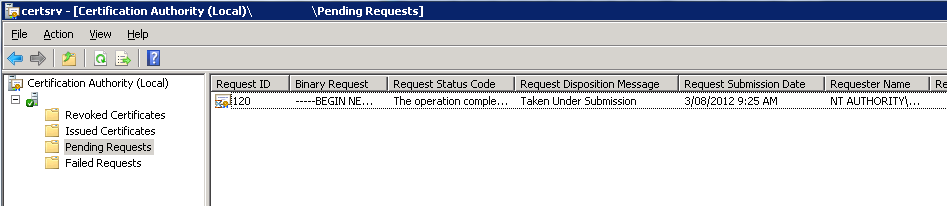
- There should be a request matching the ID you were given in the previous steps, right click on it and click All Tasks -> Issue
- Go back to your remote connection to the agent
- Click Home on the Certificate Services screen
- Click View the status of a pending certificate request
- Click the blue link – it should only show you yours
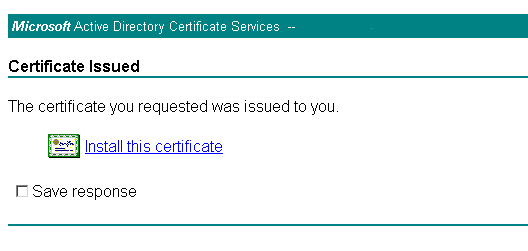
- Click Install this certificate
- Click yes to install it
- On the Agent run mmc.exe
- Click
File -> Add/Remove Snap In - Add
Certificatesand select theMy user accountoption.` - Add another
Certificatesbut this time selectComputer accountthenLocal computer - Click OK
- Expand the two trees like this:
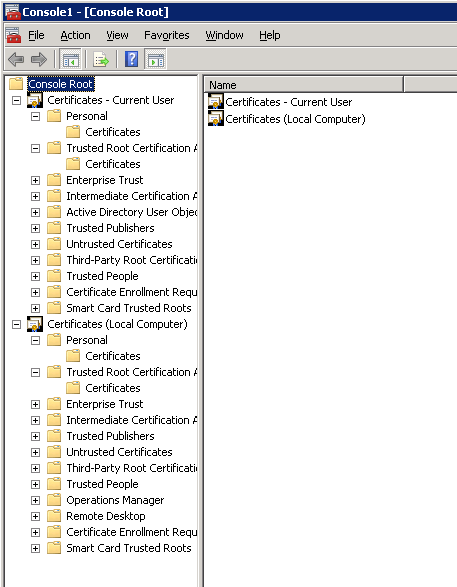
- Under
Certificates – Current user -> Personal -> Certificatesyou’ll find the client certificate. - Drag that to the matching folder under
Certificates (Local Computer) - Under
Certificates – Current user -> Trusted Root Certification Authorityyou’ll find the root CA certificate. It should have the same name as the Root CA hostname. - Right click on the certificate you imported previously and click copy.
- Ensure the expiration date of the one you’re working on has the correct expiration date – it should be 02/08/2027. (If it’s expired, hello future!)
- Go into the matching
Trusted Root Certification Authoritiesfolder under Certificates (Local Computer) and right click->paste the cert into there. - Go to
Certificates (Local Computer) -> Personal -> Certificatesand on the certificate you just dragged in there, thenRight click -> All Tasks -> Export - Click next, select Yes export the private key and click next
- The export file format should be PKCS #12 (.PFX), don’t tick anything in the boxes.
- Click next
- Enter a simple password you’ll remember and click next.
- Save the file somewhere you can navigate easily to via command prompt.
- Click next then Finish
- Open a command prompt as administrator (right click on it and click run as administrator)
- Navigate to where you put the key
- Run
MOMCertImport.exe [keyfile], substituting[keyfile]for the filename that you just exported.- 32-bit servers, run it from the SupportTools\i386 folder
- 64-bit servers, run it from the SupportTools\AMD64 folder
- It’ll ask for the password, type it in and press the enter key. After a few seconds (it won’t show that it’s doing anything) it will have completed. *After a few minutes check the event log on the client for events with ID 20053, this will show that it’s working. The logs are in the Operations Manager listings.
- Other than deleting any files on the file system you’ve created (the key files are insecure and shouldn’t be left lying around) check in the SCOM Console to ensure monitoring is working and you’re all done.