Every 18 minutes, give or take ten seconds the Splunk heavy forwarder we run was spontaneously crashing. There had been no change in traffic or other conditions that we knew about on the ESX host the server runs on.
The operating system is Debian 7.2 x86_64, installed from the netinst ISO with a very minimally modified install, and the logs weren’t showing the OOM errors I’d been fighting with previously - 2Gb of memory for Splunk is never enough.
[Read More]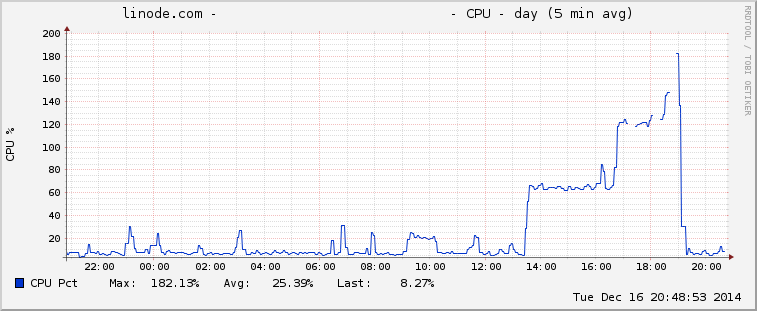
 A dog, his bowl and some bones
 A
 A bobsled, ready for fun!

 A man with a bag of jewels
 A young Luke Skywalker ready for adventure!
 A remote control car!
 An X-34 Landspeeder